A hash is a value for checking data
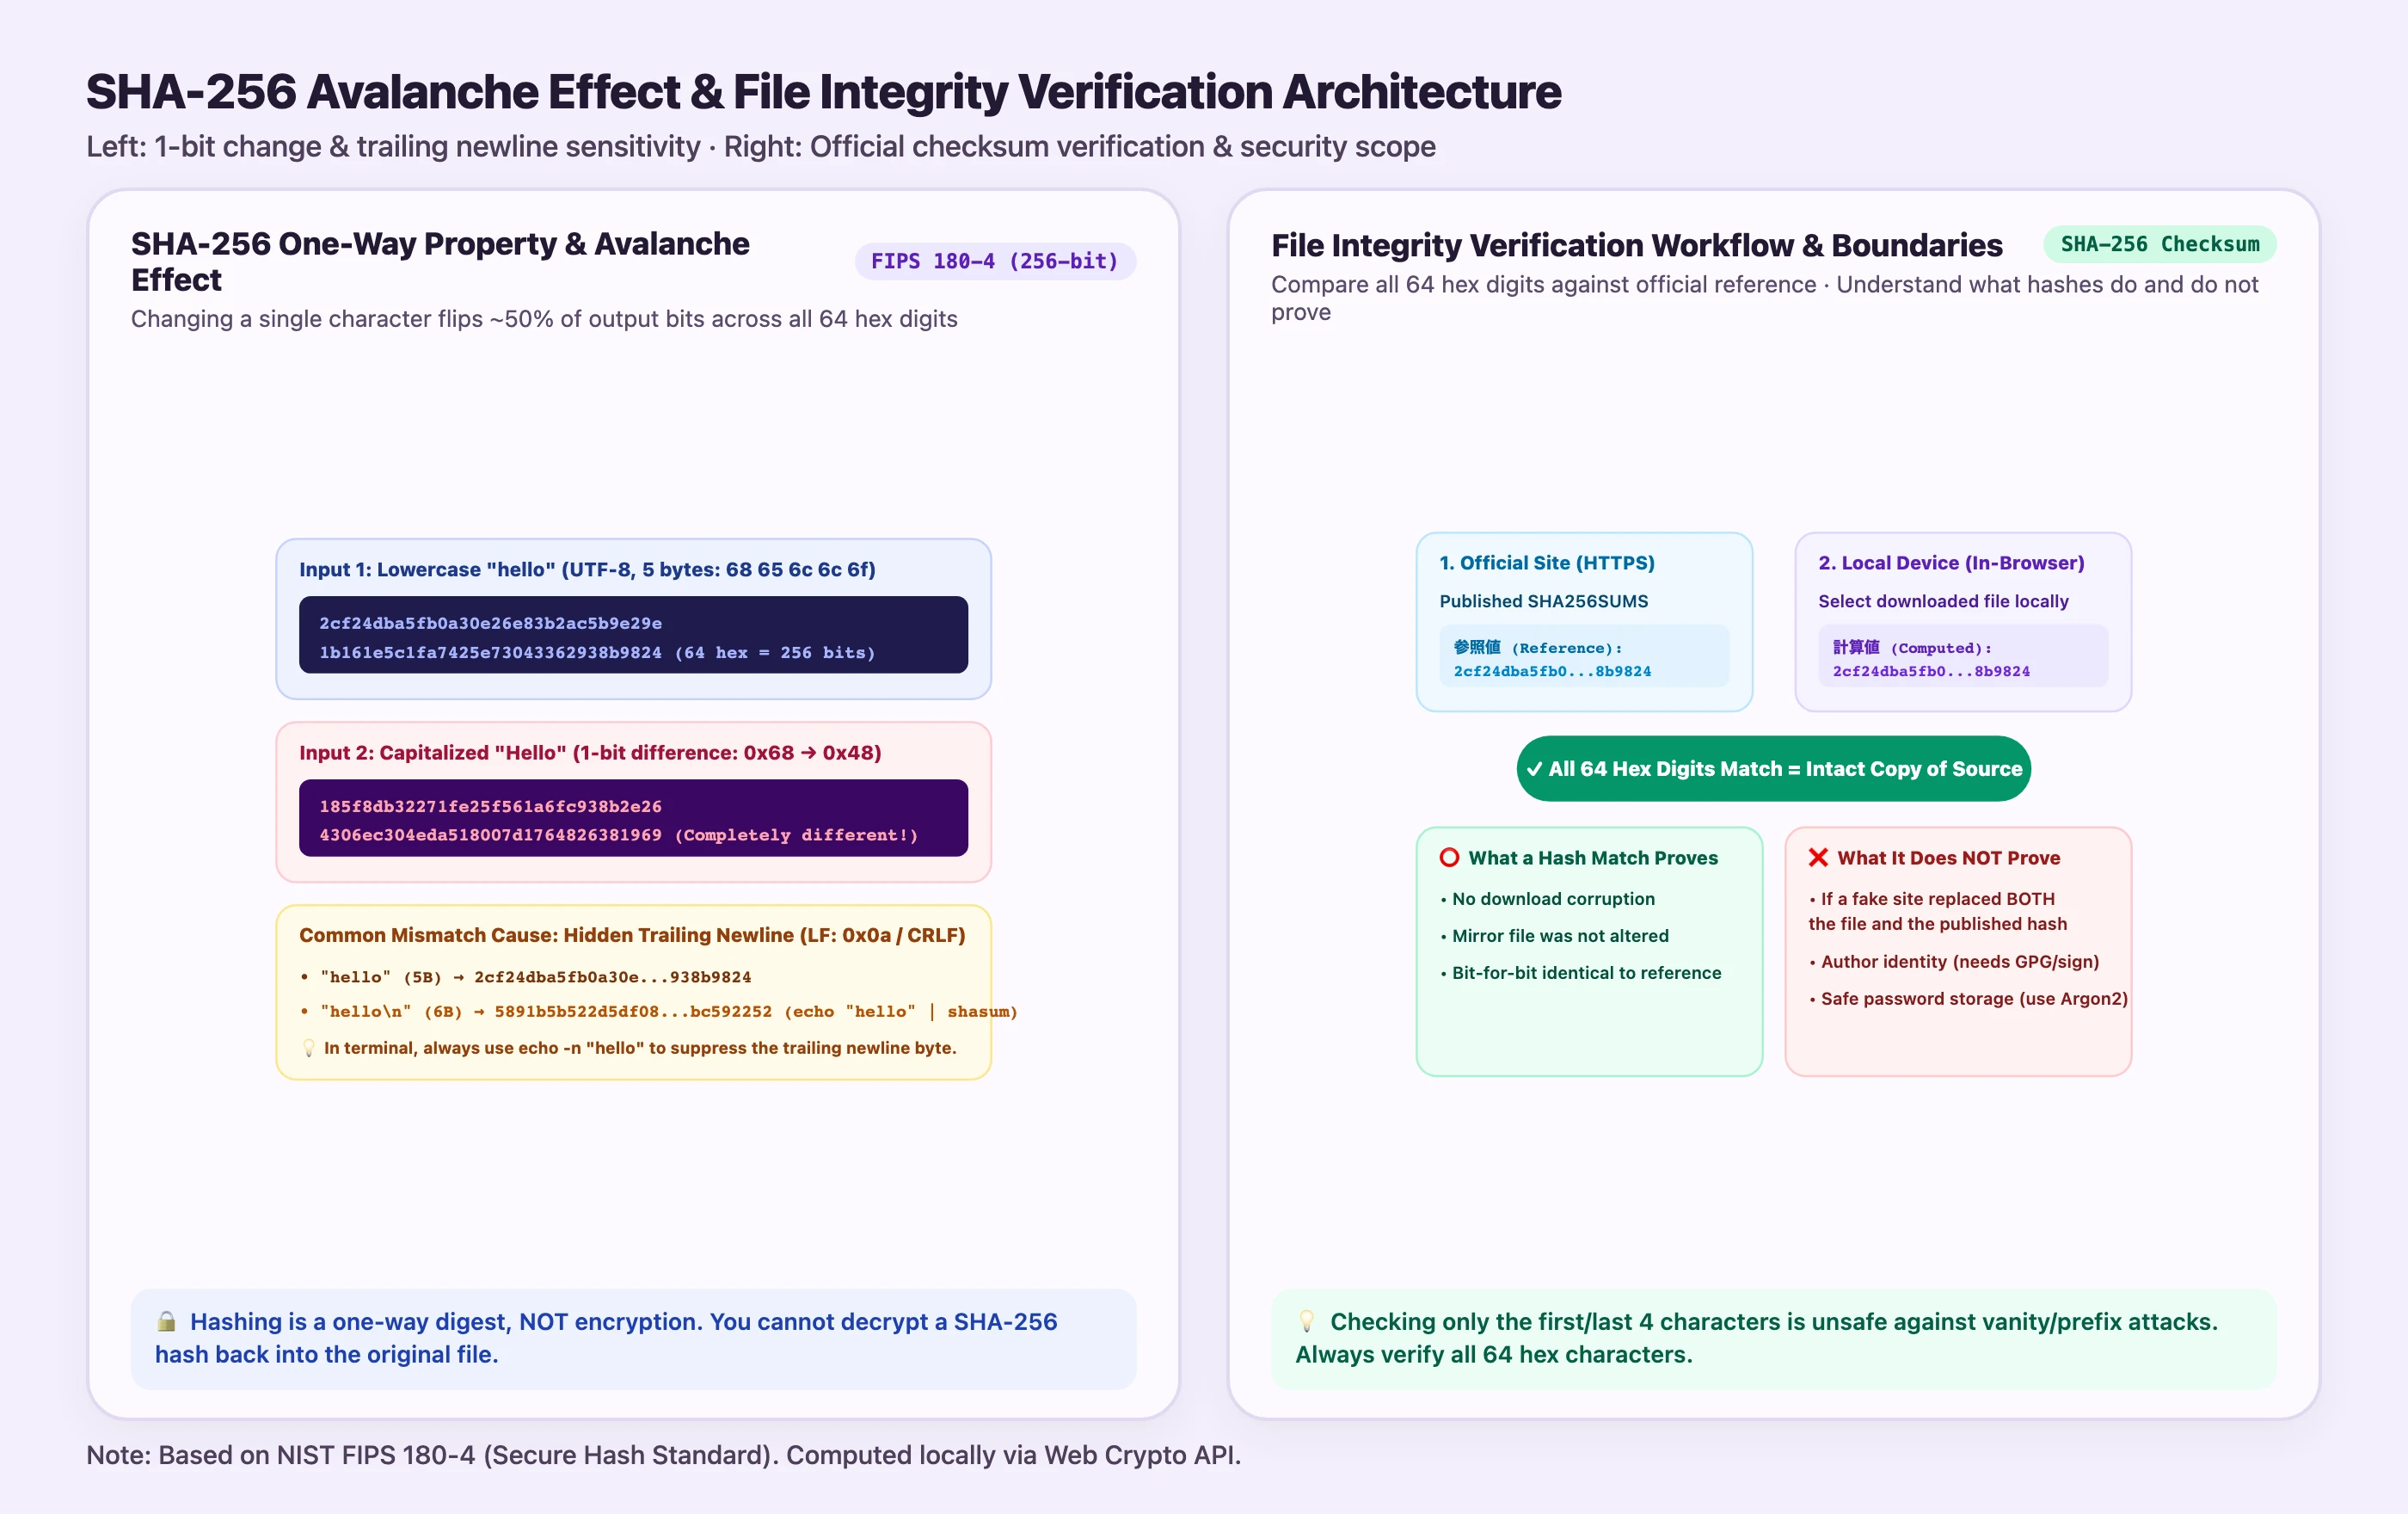
SHA-256 maps input bytes to 256 bits, displayed as 64 hexadecimal digits. Identical bytes produce the same hash. A small change normally gives a very different value, but collisions are not mathematically impossible.
The hash generator computes text and file hashes in the browser. It is not encryption and has no decryption operation. Predictable inputs can nevertheless be identified by comparing hashes of candidate values.
Check the SHA-256 example
The UTF-8 text hello, lowercase and without a trailing newline, gives:
2cf24dba5fb0a30e26e83b2ac5b9e29e1b161e5c1fa7425e73043362938b9824A trailing space or newline changes the bytes. When values differ, check capitalization, encoding, BOM, line endings and file version.
Comparison of Hash Algorithms (MD5, SHA-1, and SHA-2 Family)
Based on NIST FIPS 180-4 (Secure Hash Standard), the table below compares output lengths, collision-resistance status, and appropriate use cases.
| Algorithm | Bit Length | Hex Digits | Collision Resistance Status | Appropriate Use Cases & Limitations |
|---|---|---|---|---|
| MD5 | 128-bit | 32 chars | Broken (practical collisions in seconds) | Legacy accidental corruption checks only; never use for security or tamper detection |
| SHA-1 | 160-bit | 40 chars | Deprecated (SHAttered collision in 2017) | Legacy Git object IDs and backward compatibility; do not use for new security designs |
| SHA-256 | 256-bit | 64 chars | Recommended Standard (FIPS 180-4) | Software installer checksums, TLS certificates, digital signatures, file integrity |
| SHA-384 | 384-bit | 96 chars | Recommended (High Security) | Fast 64-bit word arithmetic, Subresource Integrity (SRI), high-assurance TLS suites |
| SHA-512 | 512-bit | 128 chars | Recommended (Maximum Digest) | Official Linux ISO checksum files (SHA512SUMS), long-term archival verification |
Verify a downloaded file
- Obtain the algorithm and expected digest from a trustworthy publisher page or signed information.
- Select the same algorithm and read the intended file.
- Compare every digit, not just the beginning and end. Hexadecimal letter case does not change the value.
- If it differs, check the version and filename before using the file or downloading it again.
A match checks integrity against that reference. If an attacker can replace both the file and the published digest, the comparison cannot expose that substitution. A hash match alone proves neither publisher authenticity nor absence of malware.
Built-in OS Terminal Commands for SHA-256 Verification
Alongside the browser-based hash generator, you can verify multi-gigabyte disk images directly from your operating system terminal:
| Operating System | Terminal Command | Output Notes |
|---|---|---|
| macOS (zsh / bash) | shasum -a 256 filename.iso |
Prints the 64-character lowercase hex digest followed by the filename |
| Windows (PowerShell) | Get-FileHash .\filename.iso -Algorithm SHA256 |
Prints the 64-character uppercase Hash property (case-insensitive match) |
| Linux (Ubuntu / Debian) | sha256sum filename.iso or sha256sum -c SHA256SUMS |
Supports automated batch verification against a published SHA256SUMS manifest |
Choose the stated algorithm
Use the algorithm named by the publisher, such as SHA-256. SHA-1 can appear in legacy compatibility checks but should not be chosen for new designs requiring collision resistance. Digests from different algorithms are not interchangeable.
Password storage needs a dedicated design
Plain SHA-256, even with a salt added, is not a suitable password-storage design. Implementers should use a dedicated password-hashing scheme such as Argon2id with appropriate parameters and current OWASP guidance. This utility is not an authentication system or a password vault.
Frequently asked questions
Can a hash be converted back to text?
There is no general reverse conversion. Guessable inputs can still be identified by candidate comparison, so hashing alone does not necessarily keep them secret.
Must I compare the whole digest?
Yes. Compare all 64 hexadecimal digits for SHA-256. A partial match is not a substitute for checking the full digest.