Start with length, randomness and a different password for each account
Use a long, unpredictable password for each service and store it in a password manager. Avoid names, birthdays, sequences and examples published in an article. Length alone does not protect you from phishing or a compromised device.
The password generator accepts 8–64 characters and defaults to 16. Choose a longer value when the destination allows it, and check which symbols it accepts. Keep the generated value out of screenshots and public documents.
What the NIST length requirements actually mean
NIST SP 800-63B-4 addresses authentication-system implementers. It requires at least 15 characters for a password used as a single factor and permits a minimum of 8 when it is part of multifactor authentication. This is not a statement that an eight-character password is safe for every account.
The guidance does not require composition rules or periodic changes without evidence of compromise. Avoiding common and compromised passwords matters more than repeatedly making predictable variations. Follow the destination’s input requirements when it has its own rules.
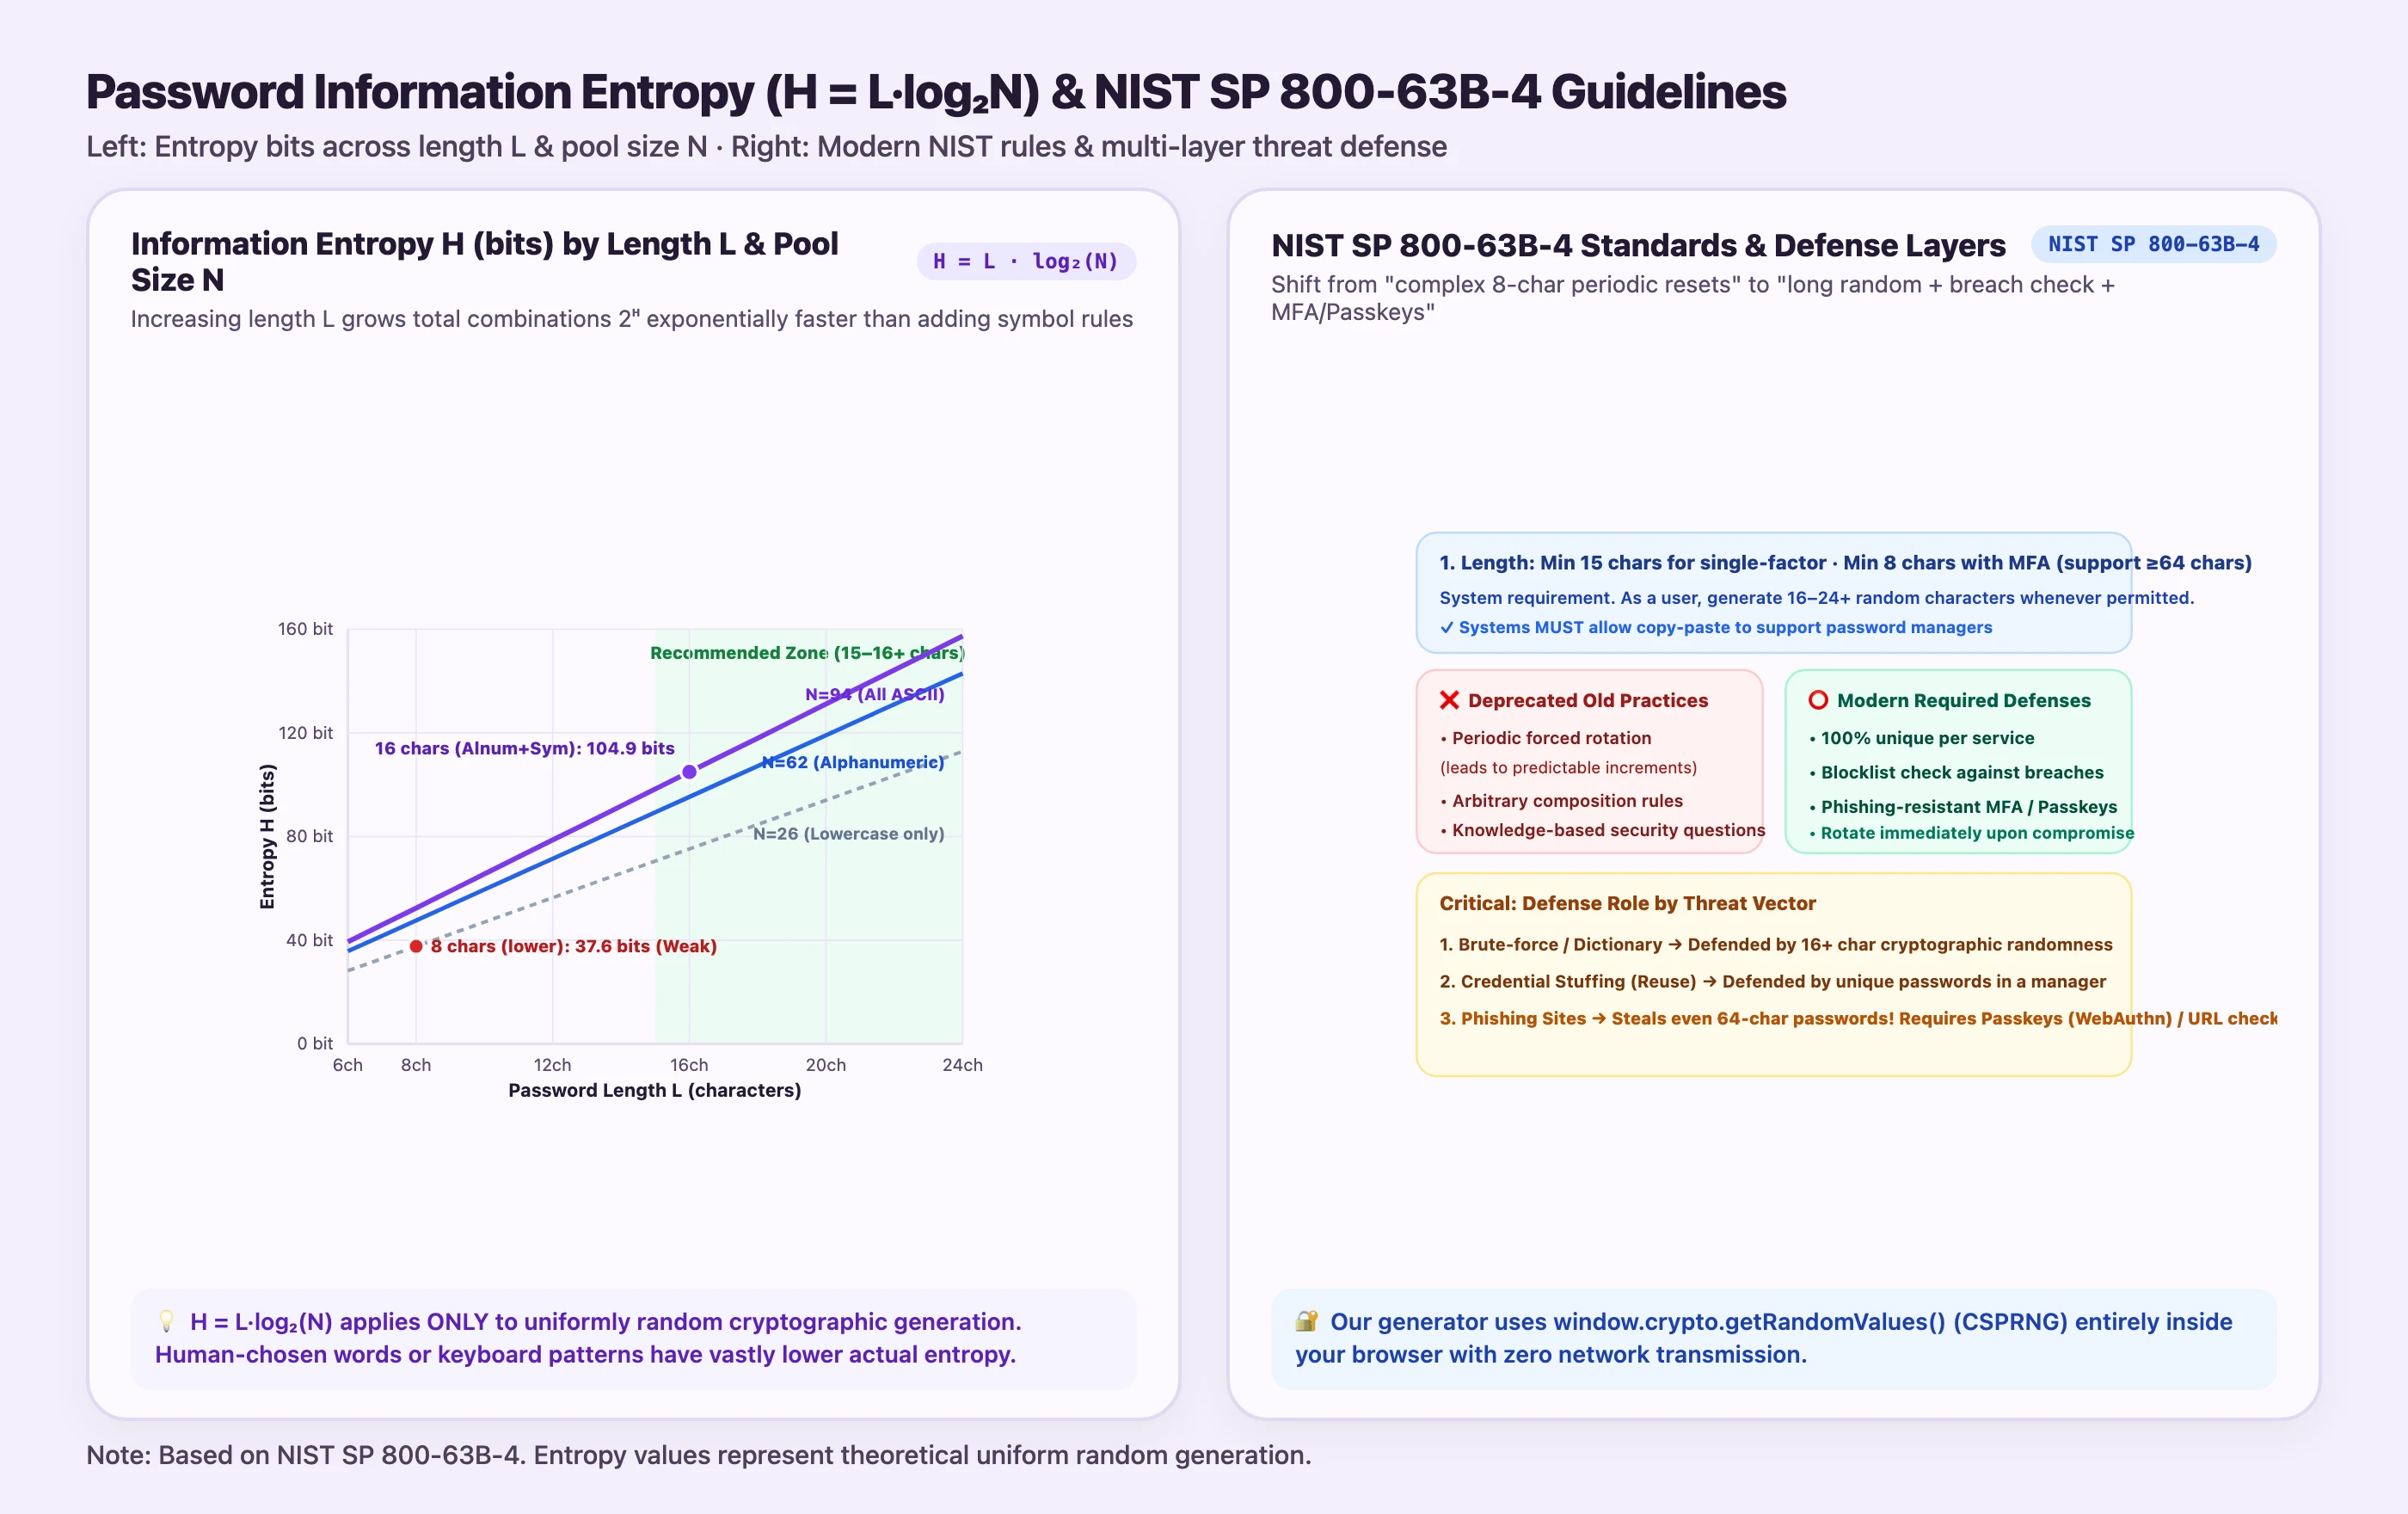
Information Entropy Reference Table (Uniform CSPRNG Selection)
When characters are drawn independently and uniformly using a cryptographically secure pseudo-random number generator (crypto.getRandomValues()), the search-space entropy H (in bits) is:
where L is the password length and N is the character pool size. Extending length L increases the candidate space 2H exponentially faster than expanding the character pool alone (note: entropy measures uniform search space and is not a guaranteed cracking time).
| Character Pool (Size N) | Bits / Char log₂(N) | 8 Chars | 12 Chars | 16 Chars | 20 Chars | 24 Chars |
|---|---|---|---|---|---|---|
| Digits only (0–9, N=10) | 3.32 bits | 26.6 bits | 39.9 bits | 53.2 bits | 66.4 bits | 79.7 bits |
| Lowercase only (a–z, N=26) | 4.70 bits | 37.6 bits | 56.4 bits | 75.2 bits | 94.0 bits | 112.8 bits |
| Alphanumeric (A–Z, a–z, 0–9, N=62) | 5.95 bits | 47.6 bits | 71.5 bits | 95.3 bits | 119.1 bits | 142.9 bits |
| Full ASCII Printable (N=94) | 6.55 bits | 52.4 bits | 78.7 bits | 104.9 bits | 131.1 bits | 157.3 bits |
Summary of NIST SP 800-63B-4 Password Guidelines
| Requirement Area | Outdated Legacy Practice | NIST SP 800-63B-4 Standard |
|---|---|---|
| Minimum Length | 6–8 characters across all contexts | At least 15 characters for single-factor; at least 8 characters with MFA |
| Maximum Allowed Length | Truncating or rejecting at 12–16 chars | Support at least 64 characters and allow password-manager paste |
| Composition Rules | Forcing arbitrary symbol/digit mixtures | Do not impose composition rules; screen against breached password blocklists |
| Periodic Rotation | Mandatory 60- or 90-day expiration | Do not force periodic changes without evidence of a credential compromise |
Generate, save and protect an account
- Check the service’s length limit and allowed symbols.
- Choose a length and character pools, then generate. Selecting a pool makes its characters available; it does not guarantee that every selected type appears.
- Save the new, unique value in a password manager.
- Enable multifactor authentication or a passkey where supported and keep recovery options accessible.
The tool uses the browser’s crypto.getRandomValues(). Its strength indicator is a rough estimate based on length and selected character types, not a cracking-time calculation or a guarantee against compromise.
Is any memorable passphrase strong?
Famous quotations, lyrics and hand-picked word sequences may be predictable. If you prefer passphrases, consider a manager that randomly selects words from a word list. This site’s generator produces character strings; it does not have a word-list mode.
If you suspect a leak
Open the official app or a URL you have independently checked. Follow the provider’s recovery instructions, change reused passwords elsewhere, and review active sessions and recovery settings. MFA reduces risk but is not infallible: entering a one-time code into a phishing site can still compromise an account.
Frequently asked questions
Is a 16-character password unbreakable?
No. Risk depends on how it was generated, the provider’s storage, attack conditions and exposure to reuse or phishing. A universal table of “years to crack” would hide those assumptions.
Must I change it every month?
Change compromised, reused or weak values. Merely changing a trailing number on a schedule can leave predictable patterns intact. Ask your administrator about any organizational requirements.
Is the generated password sent to a server?
Generation happens in the browser and the implementation does not transmit the generated value. Shared devices, extensions and clipboard history still need separate consideration.